Download

Silent Leak Killer

You've already sent it.

One ordinary session. Secrets left your machine for an LLM. Nobody was careless. LocalGuard stops the next ones before they leave.

macOS · Linux · Windows. Installs in about 2 minutes, no licence needed

100% local Zero telemetry Under 50ms

Measured session

This is what one session looked like.

Not a lab demo. Not a promise of what "might" leak. Numbers from a real LocalGuard run.

669
secrets caught
138
requests
67%
requests contained secrets
109 MB
scanned

Measured session. Your numbers will differ. The pattern usually does not.
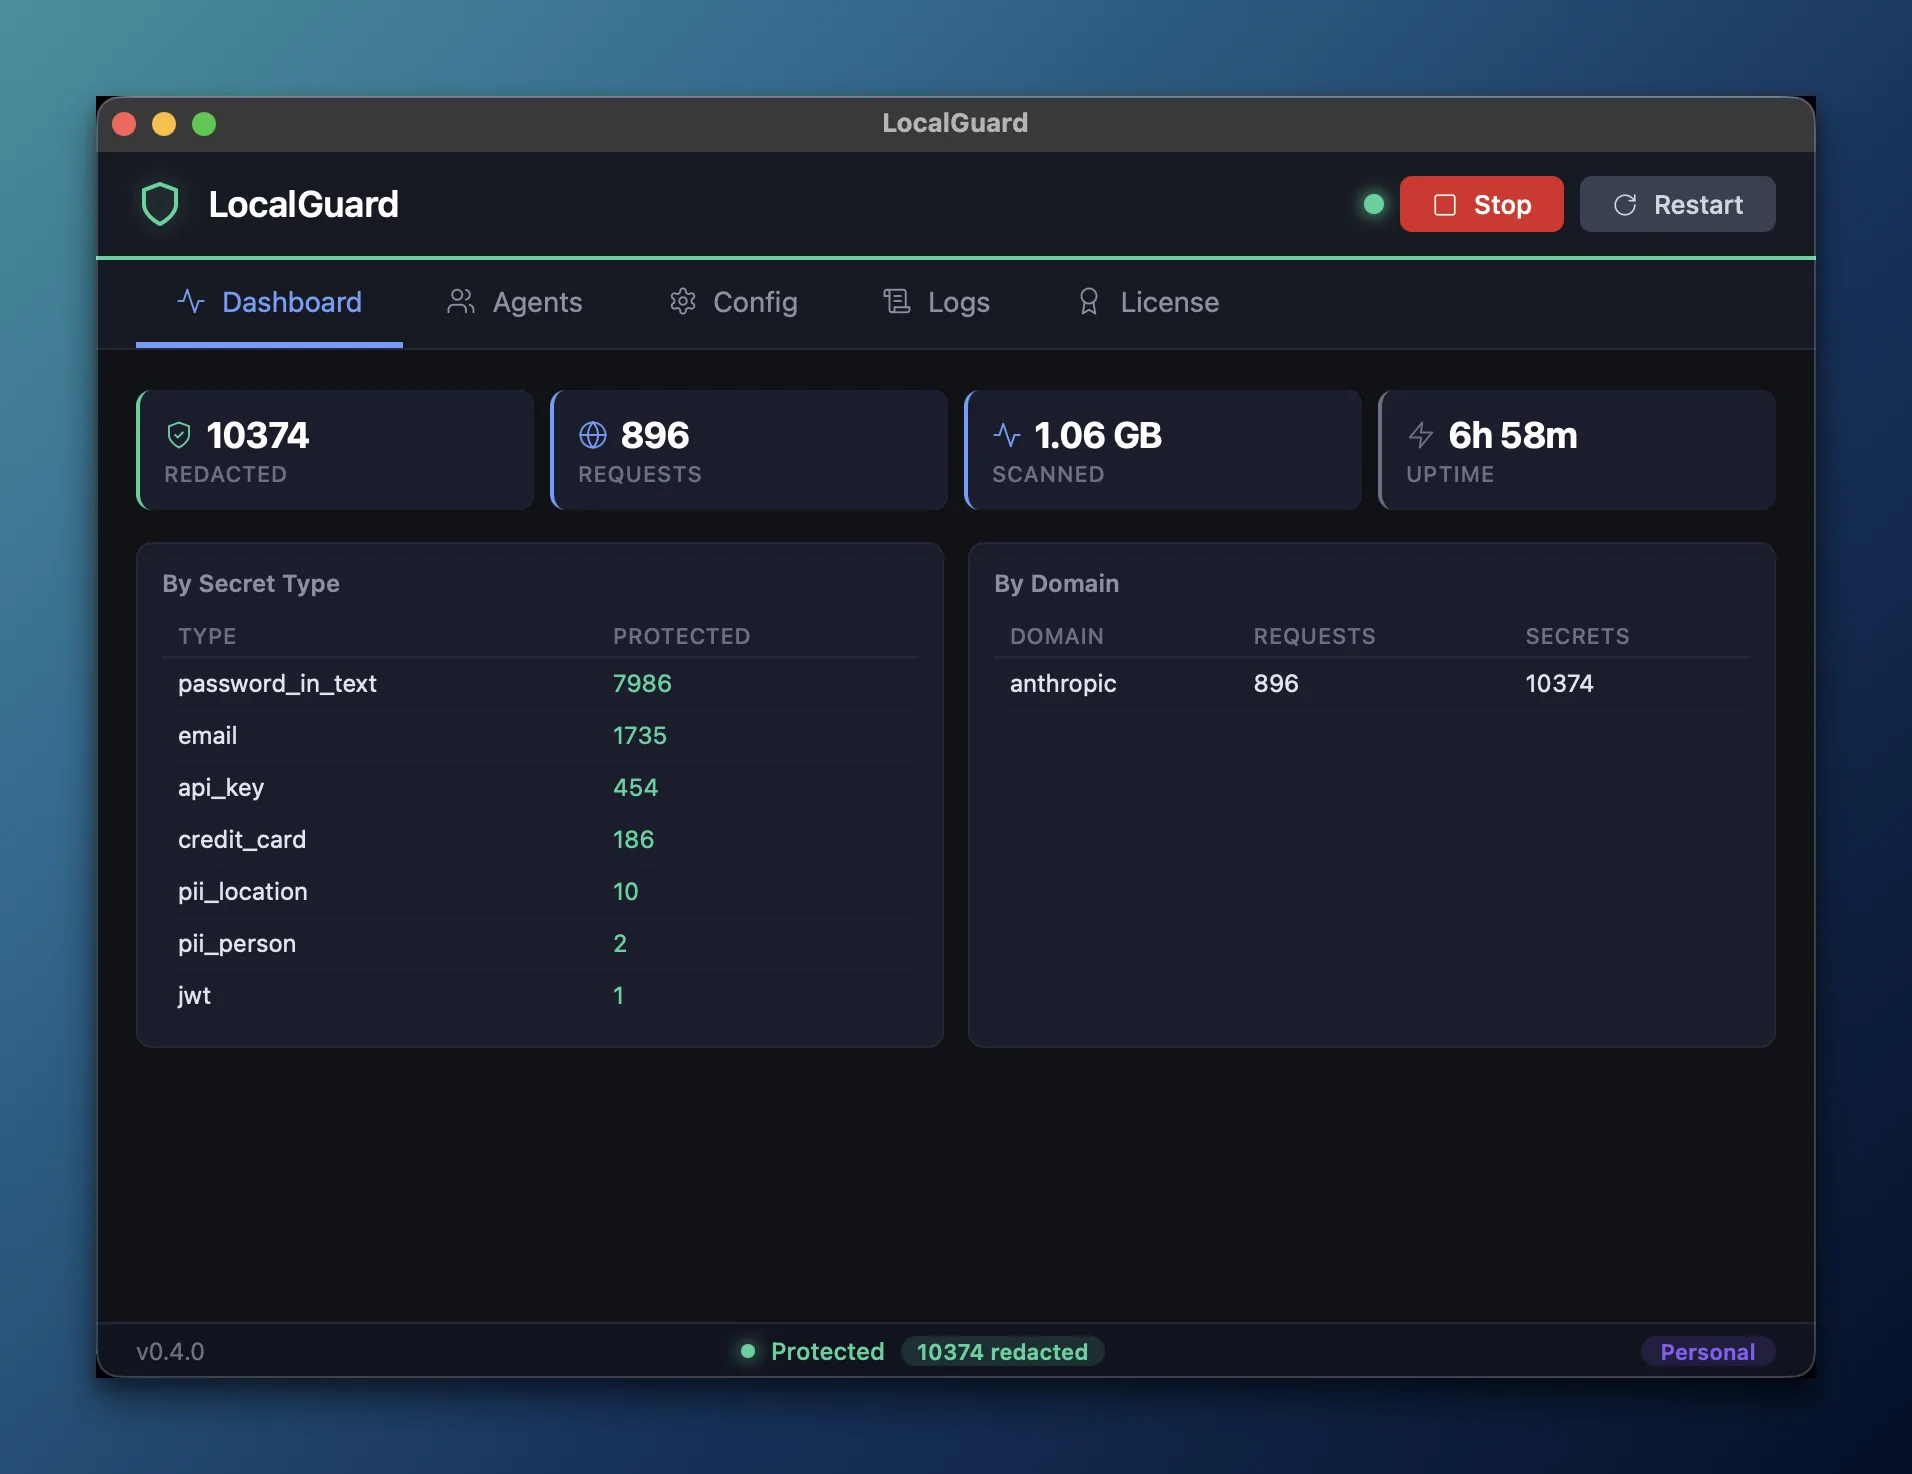
LocalGuard live dashboard and per-event logs
Live activity: which tool sent what, where Real product screenshot
Another real run: 10 374 values · 896 requests · 1.06 GB

What already left

Once it's in the model, it's out of your hands.

Access

API keys. AWS. GitHub tokens. JWT. PEM. Whoever has them walks in as you.

Money

Cards. Wallets. Payment tokens. Quiet theft does not need drama.

Clients

Emails. Phones. Names. Places. Data that was never yours to expose.

Business

The prompt that explains how you work. Competitors and attackers read the same text.

Careful people still leak. LocalGuard exists because careful is not enough.

Local by design

A proxy on your machine. Nothing ships to our cloud. There is no cloud scan.

01

Sit in the middle

LocalGuard runs in your menu bar. AI tools talk through it to model providers.

02

Scan and replace

Secrets become placeholders before the request leaves. All on device. Under 50ms.

03

Restore on the way back

Responses land clean. Your workflow stays intact. The provider never saw the real values.

Written in Rust Zero telemetry No cloud scanning €5 for the first month

See it happen

Same prompt. Two outcomes.

Without a subscription LocalGuard shows what leaves. With one, nothing does.

Detect-only: every secret is marked, and it still leaves
Your prompt
What would leave

            
The app starts in detect-only mode, so you see your own leaks before you pay anything.

Pricing

See your leaks for free. Stop them for €5.

One computer
LocalGuard
€5 first month

then €49/year + VAT · cancel anytime

  • API keys, tokens, private keys, AWS keys
  • Passwords, including in URLs
  • Cards, IBAN, crypto wallets
  • Emails and phone numbers
  • On-device AI for names and places
  • Answers come back with the real values
  • Move to a new computer any time
Start for €5

Stripe · VAT added at checkout · €5 today, €49 after 30 days, then yearly.

Before you subscribe
Detect-only

The app is free to download.

  • Shows every secret your AI tools send
  • Which tool, which provider, when
  • Redacts nothing
Download

Turn protection on from the app whenever you are ready.

Teams, self-hosted and CLI installs: support@localguard.me.

Works where you already work

Connect 24 AI tools in one click.

33 tool families audited. An alphabetical catalog. Connect and Disconnect buttons, with no config files to edit by hand.

Aider Claude Code Cline Codex CommandCode Continue Crush DeepSeek Harness Gemini CLI Goose Hermes Kilo Code Letta MimoCode omp OpenClaw OpenCode OpenHands Pi ProtoAgent Qwen Code shell-gpt Strix Zed

Coverage depends on the tool's local mode and provider. For example, Codex supports API-key and ChatGPT-plan login; Gemini CLI requires API-key login. The app explains the supported mode for every tool. Restart the tool after connecting.

Disconnect restores the original routing settings and preserves your credentials, models and later edits. Project settings, shell variables and cloud execution can use separate routes.

Why 9 audited families have no automatic connection
  • agy (Antigravity): no supported local model address override confirmed.
  • CodeGPT: no verified external settings writer for the editor extension.
  • Cursor: model requests pass through Cursor's servers.
  • Kiro / Amazon Q: no verified local model address override for cloud features.
  • Lemonade: runs models locally and serves other clients; local inference needs no cloud proxy.
  • Roo Code: no verified external settings writer for its private editor storage.
  • Warp: cloud inference cannot reach LocalGuard on your computer.
  • Windsurf / Devin: no verified local model address override for cloud features.
  • ZCode: custom addresses exist in its interface, but no verified external-write format.

See connection modes and setup instructions →

Menu bar app for macOS, Linux, and Windows. Written in Rust. Scans stay on your machine.

Questions worth answering

FAQ

No. Scanning runs on your machine. There is no cloud scanning and no telemetry.
LocalGuard runs in detect-only mode: it shows which secrets your AI tools sent, to which provider and when, and redacts nothing. Turn protection on from the app when you are ready.
€5 for the first month, then €49 a year, plus VAT, charged automatically. Cancel any time from the app; protection stays on until the end of the paid period. One computer at a time — activating on a new one moves the subscription.
Redaction is local and built to stay under 50ms. Your tools keep talking to the same providers.
24 local integrations, including Claude Code, Codex, OpenCode, Pi, Hermes, Goose, OpenClaw and MimoCode. The app detects installed tools and connects supported local modes in one click. Each tool explains its provider and login limitations. Cloud features, project overrides and custom settings can use separate routes. See the full alphabetical catalog.
Because ordinary sessions still leak. Detect-only shows you what left. Protection stops it before it leaves.

Stop the next leak before it leaves.

The download is free: until you subscribe, LocalGuard shows what leaks and redacts nothing.